



Context In the last few days, several businesses, including aviation and banking sectors, experienced significant disruptions due to issues with Microsoft services. This outage affected various cloud-based services, including Microsoft 365, Azure, and Teams. The interruptions were caused by a combination of network configuration changes and infrastructure issues within Microsoft's global network (https://www.reedsmith.com/en/perspectives/2024/02/business-interruption-claims-in-2024-a-global-perspective) (https://status.cloud.microsoft/#:~:text=URL%3A%20https%3A%2F%2Fstatus,100). The outage highlighted the increasing reliance of global industries on cloud services and the significant impact such disruptions can have on business operations, from communication breakdowns to halted transactions (https://www.businesswire.com/news/home/20240116375142/en/Allianz-Risk-Barometer-A-Cyber-Event-Is-the-Top-Global-Business-Risk-for-2024). While Microsoft worked to resolve the issues, it underscored the importance of robust cyber risk management and contingency planning in mitigating the effects of such outages (https://www.nortonrosefulbright.com/en/knowledge/publications/20530078/the-cyber-risks-faced-by-the-aviation-industry---ten-things-to-know). The recent Microsoft outages, which disrupted services like Microsoft 365, Teams, and Outlook, were primarily caused by a series of technical and security issues. Initially, Microsoft identified that a "wide-area networking (WAN) routing change" led to connectivity problems. This change triggered issues with network latency and timeouts, affecting how packets were forwarded across Microsoft's global network. This impacted users' ability to access various cloud services, including Azure, SharePoint, and OneDrive (https://www.bankinfosecurity.com/microsoft-365-cloud-service-outage-disrupts-users-worldwide-a-21017) (https://www.techradar.com/news/this-is-what-caused-the-recent-huge-microsoft-365-and-teams-outage). Additionally, Microsoft faced cyber risks, particularly distributed denial-of-service (DDoS) attacks. These attacks, launched by a group known as Storm-1359, aimed to disrupt services by overwhelming Microsoft's infrastructure with malicious traffic. The DDoS attacks targeted layer 7 of the OSI model, affecting HTTP(S) traffic and causing resource exhaustion and slowdowns (https://msrc.microsoft.com/blog/2023/06/microsoft-response-to-layer-7-distributed-denial-of-service-ddos-attacks/). To mitigate these issues, Microsoft rolled back the problematic network changes and implemented additional protections to prevent similar disruptions in the future. These measures included enhancing their Web Application Firewall (WAF) and adding stricter controls on network command executions to avoid unintended consequences from network changes (https://www.bankinfosecurity.com/microsoft-experiences-second-major-cloud-outage-in-2-weeks-a-21134) (https://www.techradar.com/news/this-is-what-caused-the-recent-huge-microsoft-365-and-teams-outage). In recent days, significant disruptions in Microsoft services have caused major headaches for businesses worldwide. Industries ranging from aviation to banking found themselves grappling with unexpected downtime, impacting critical operations and highlighting a growing reliance on cloud-based services. This article explores whether Microsoft should be held legally accountable for failing to ensure business continuity for its global customers. The Outage and Its Impacts The recent Microsoft outages affected a range of cloud services, including Microsoft 365, Azure, and Teams. These disruptions were triggered by a combination of network configuration changes and infrastructure issues within Microsoft’s global network. Specifically, a "wide-area networking (WAN) routing change" led to severe connectivity problems. This change caused network latency and timeouts, disrupting the forwarding of data packets across Microsoft's global network. As a result, users experienced significant issues accessing cloud services such as Azure, SharePoint, and OneDrive. In addition to technical glitches, Microsoft also faced cyber threats, particularly distributed denial-of-service (DDoS) attacks. A group known as Storm-1359 targeted Microsoft’s infrastructure with malicious traffic, aiming to exhaust resources and slow down services. These attacks impacted layer 7 of the OSI model, affecting HTTP(S) traffic and causing further disruptions. The Importance of Business Continuity These outages underscore the critical role that cloud services play in modern business operations. From communication breakdowns to halted transactions, the ripple effects of such disruptions can be severe. The aviation and banking sectors, in particular, experienced significant operational impacts, illustrating the high stakes involved. As businesses increasingly rely on cloud services for their day-to-day operations, the importance of robust cyber risk management and contingency planning becomes more apparent. Legal and Ethical Considerations Given the scale and impact of these disruptions, the question arises: should Microsoft be sued for not ensuring business continuity? On one hand, businesses rely on service level agreements (SLAs) with cloud providers like Microsoft to guarantee a certain level of uptime and reliability. When these expectations are not met, it can lead to substantial financial losses and operational challenges. Businesses may argue that Microsoft failed to uphold its end of the agreement, warranting legal action to recover damages. On the other hand, the complexity of managing a global cloud infrastructure means that occasional outages are inevitable. Microsoft did take immediate steps to mitigate the issues, rolling back problematic network changes and enhancing protections against future disruptions. These efforts demonstrate a commitment to resolving the issues and improving service reliability. Cyber Risk Management and Contingency Planning The outages highlight the need for businesses to adopt comprehensive cyber risk management strategies and contingency plans. Relying solely on a single cloud provider can expose businesses to significant risks. Diversifying cloud services and implementing robust backup systems can help mitigate the impact of such outages. Additionally, regular testing and updating of contingency plans can ensure that businesses are better prepared to handle unexpected disruptions. Conclusion While the recent Microsoft outages have caused significant disruptions, suing the tech giant may not be the most effective solution. Instead, businesses should focus on enhancing their own cyber risk management and contingency planning efforts. By diversifying cloud services and implementing robust backup systems, businesses can better protect themselves against future outages. At the same time, cloud providers like Microsoft must continue to improve their infrastructure and security measures to minimize the risk of such disruptions and maintain customer trust. The recent events serve as a stark reminder of the interconnected nature of modern business operations and the importance of resilience in the face of unexpected challenges. References https://www.reedsmith.com/en/perspectives/2024/02/business-interruption-claims-in-2024-a-global-perspective https://status.cloud.microsoft/#:~:text=URL%3A%20https%3A%2F%2Fstatus,100). (https://www.businesswire.com/news/home/20240116375142/en/Allianz-Risk-Barometer-A-Cyber-Event-Is-the-Top-Global-Business-Risk-for-2024 https://www.nortonrosefulbright.com/en/knowledge/publications/20530078/the-cyber-risks-faced-by-the-aviation-industry---ten-things-to-know https://www.bankinfosecurity.com/microsoft-365-cloud-service-outage-disrupts-users-worldwide-a-21017 https://www.techradar.com/news/this-is-what-caused-the-recent-huge-microsoft-365-and-teams-outage https://msrc.microsoft.com/blog/2023/06/microsoft-response-to-layer-7-distributed-denial-of-service-ddos-attacks/
by Youness El Kandoussi | 2 years ago | 0 Comment(s) | 1219 Share(s) | Tags :
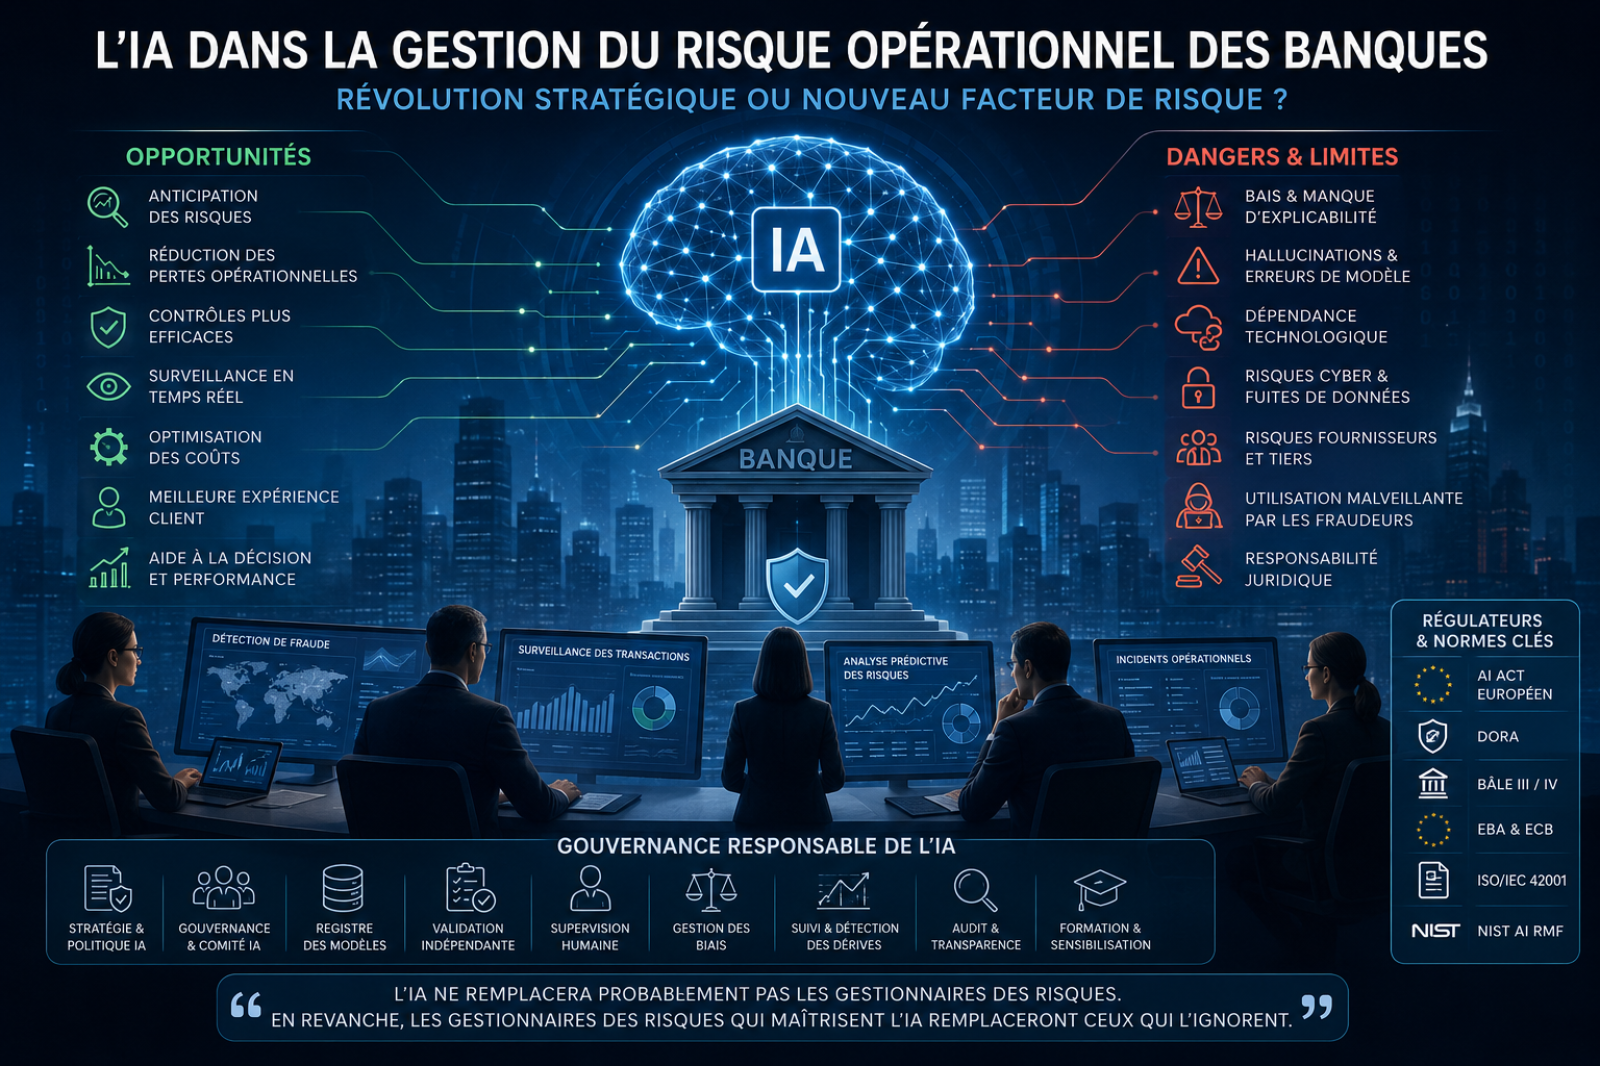
Comment construire une gouvernance de l'IA qui inspire confiance, respecte les exigences r glementaires et cr e un avantage concurrentiel durable. Une salle des march s qui ne dort jamais Il y a dix ans, un incident op rationnel majeur mettait plusieurs heures à être d tect . Aujourd'hui, dans certaines banques, un modèle d'IA identifie une anomalie de flux de paiement en quelques secondes, la corrèle avec des dizaines de signaux faibles, et alerte l' quipe de contrôle permanent avant même qu'un client ne s'en aperçoive. Ce basculement n'est pas anecdotique : il red finit la nature même du m tier de gestionnaire des risques. Mais cette même technologie qui d tecte la fraude en temps r el peut aussi se tromper en toute confiance, halluciner un chiffre inexistant dans un rapport r glementaire, ou reproduire un biais discriminatoire à grande chelle. L'IA n'est donc ni un simple outil d'efficacit , ni une menace à carter par principe. C'est un nouveau territoire de risque op rationnel à part entière, qui doit être gouvern avec la même rigueur que le risque de cr dit ou le risque de march . C'est pr cis ment cette double lecture — acc l rateur de r silience et risque mergent — qui doit structurer la r flexion des dirigeants bancaires en 2026. Pourquoi l'IA devient incontournable dans les banques Plusieurs pressions convergentes expliquent l'acc l ration actuelle. La pression r glementaire s'intensifie. DORA impose depuis janvier 2025 un cadre strict de gestion du risque ICT, de reporting d'incidents et de tests de r silience op rationnelle num rique pour l'ensemble des entit s financières europ ennes. En parallèle, le règlement europ en sur l'IA (AI Act) est entr en vigueur en août 2024, avec des obligations de plus en plus contraignantes pour les systèmes d'IA à haut risque — dont plusieurs cas d'usage bancaires (scoring de cr dit, valuation de risque) relèvent directement. Les banques doivent d sormais d montrer, preuves à l'appui, qu'elles maîtrisent leurs modèles. La cybercriminalit et la fraude se sophistiquent. Selon les donn es cit es par Deloitte, les pertes li es à la fraude d'identit dans les services financiers ont atteint 12,5 milliards de dollars en 2024, en hausse de 25 % par rapport à 2023, port es notamment par les identit s synth tiques. L'activit frauduleuse aurait progress d'environ 21 % entre 2024 et 2025, avec d sormais une tentative de v rification sur vingt signal e comme potentiellement frauduleuse. Plus pr occupant encore : plus de la moiti des fraudes impliqueraient aujourd'hui une composante IA (deepfakes, identit s synth tiques, hameçonnage automatis ), un ph nomène qui pourrait porter les pertes li es à la fraude g n r e par IA à 40 milliards de dollars d'ici 2027. Les coûts op rationnels restent sous tension. McKinsey estime que les fonctions op rationnelles mobilisent entre 50 % et 60 % des quivalents temps plein d'une banque type, ce qui en fait un terrain naturel de transformation par l'IA, juste après la technologie et l'ing nierie. Les donn es explosent, et avec elles la capacit — ou l'incapacit — des banques à les exploiter en temps r el pour d tecter les signaux de risque. Les attentes des clients voluent vers une exp rience instantan e, personnalis e et sans friction, y compris dans la gestion des r clamations, des alertes de fraude ou des interactions avec les quipes de conformit . Les principaux cas d'usage dans le risque op rationnel D tection de fraude. Les moteurs de machine learning analysent des millions de points de donn es par transaction pour rep rer des sch mas anormaux, remplaçant progressivement les règles statiques historiques. D'après une enquête Mastercard men e avec Financial Times Longitude, 42 % des metteurs et 26 % des acqu reurs d clarent avoir vit plus de 5 millions de dollars de pertes de fraude sur deux ans grâce à l'IA, et 80 % des organisations estiment que l'IA a permis de r duire les contrôles manuels inutiles. Lutte contre le blanchiment (AML). Les modèles d'IA croisent des volumes massifs de transactions avec des bases de sanctions, des donn es de b n ficiaires effectifs et des sch mas comportementaux. Un exemple souvent cit dans l'industrie est celui d'un grand groupe bancaire international ayant d ploy une solution d'IA capable de surveiller plusieurs centaines de millions de transactions mensuelles sur des dizaines de millions de comptes, pour d tecter des r seaux de blanchiment que les approches traditionnelles peinaient à identifier. Surveillance des transactions et scoring des risques. Des modèles pr dictifs attribuent en continu un score de risque dynamique à chaque client, chaque transaction ou chaque contrepartie, permettant un pilotage proactif plutôt que r actif. Gestion des incidents op rationnels. Des systèmes d'IA classifient automatiquement les incidents, en valuent la s v rit , et orientent les quipes vers la bonne proc dure de rem diation — r duisant les d lais de d tection et de r solution. Analyse pr dictive et contrôles permanents. L'IA identifie des tendances de d rive avant qu'elles ne deviennent des incidents av r s, renforçant la première ligne de d fense. OCR intelligent et analyse documentaire. Les banques automatisent la lecture, la classification et l'extraction d'informations à partir de contrats, de dossiers KYC ou de justificatifs, r duisant drastiquement les d lais de traitement manuel. G n ration automatique de rapports r glementaires. Des outils d'IA g n rative assistent d sormais la r daction des rapports COREP, FINREP ou des dossiers de contrôle interne, en s'appuyant sur des donn es structur es et une supervision humaine. IA g n rative pour les quipes Risk et Compliance. Des « experts virtuels » internes permettent aux quipes de poser des questions en langage naturel sur les politiques internes, la r glementation ou l'historique des incidents, acc l rant la prise de d cision sans remplacer le jugement humain. Les opportunit s : une transformation mesurable Les gains ne sont plus th oriques. McKinsey value à environ 2 000 milliards de dollars la valeur annuelle totale que l'IA g n rative et l'analytique avanc e pourraient cr er dans le secteur bancaire mondial, en combinant productivit , r duction des risques et nouveaux revenus. Autre donn e significative : 70 % des banques commerciales auraient d jà adopt l'IA dans au moins une fonction cœur de m tier, et 78 % des tablissements ayant investi dans l'IA constateraient un retour sur investissement positif en moins de dix-huit mois. Concrètement, les opportunit s se d ploient sur plusieurs axes : Anticipation renforc e des risques, grâce à une surveillance continue plutôt que ponctuelle. R duction des pertes op rationnelles, par une d tection plus rapide et plus pr cise des anomalies. Qualit accrue des contrôles, avec une couverture exhaustive plutôt qu'un chantillonnage. Acc l ration des investigations, l'IA pr qualifiant les dossiers avant intervention humaine. Optimisation des coûts, notamment sur les tâches à faible valeur ajout e. R silience op rationnelle am lior e, condition d sormais explicitement attendue par les r gulateurs europ ens. Selon le rapport Deloitte sur l'adoption de l'IA dans les institutions financières europ ennes, 94 % des grandes banques et 62 % des petites banques utilisaient d jà l'IA g n rative en 2025, avec la d tection de fraude — AML et KYC compris — comme cas d'usage le plus r pandu, cit par 58 % des banques interrog es. Les dangers et les limites : l'envers du d cor Ces b n fices ne doivent pas occulter une r alit plus inconfortable : l'IA introduit une nouvelle classe de risques, à la fois techniques, thiques et juridiques. Les hallucinations restent un enjeu central pour l'IA g n rative : un modèle peut produire une r ponse plausible mais factuellement fausse, avec un niveau de confiance trompeur — un risque majeur lorsqu'il s'agit de rapports r glementaires. Les biais algorithmiques peuvent reproduire, voire amplifier, des discriminations historiques pr sentes dans les donn es d'entraînement, exposant la banque à un risque de non-conformit et r putationnel. Le manque d'explicabilit de certains modèles complexes complique la justification des d cisions auprès des r gulateurs, des clients et des auditeurs. La d pendance technologique et le risque fournisseur s'accroissent à mesure que les banques externalisent une partie de leurs capacit s d'IA à des tiers, cr ant une nouvelle forme de concentration du risque op rationnel. La cybers curit et la confidentialit des donn es deviennent des enjeux critiques : les modèles d'IA constituent eux-mêmes une nouvelle surface d'attaque. L'obsolescence des modèles, la d rive des performances dans le temps, et les erreurs de d cision qui en d coulent, exigent une surveillance continue plutôt qu'une validation ponctuelle. La responsabilit juridique reste souvent floue lorsqu'une d cision automatis e cause un pr judice. Une gouvernance insuffisante demeure, selon McKinsey, l'un des principaux freins à une adoption responsable : le niveau moyen de maturit en IA responsable a certes progress (de 2,0 à 2,3 sur une chelle de maturit entre 2025 et 2026), mais seul un tiers environ des organisations atteint un niveau de maturit lev en matière de strat gie et de gouvernance. Enfin, l'IA est d sormais aussi une arme entre les mains des fraudeurs — deepfakes, voix synth tiques, documents falsifi s — ce qui transforme la lutte antifraude en course technologique permanente. Ce qu'attendent les r gulateurs Le paysage r glementaire se densifie rapidement autour de l'IA bancaire : AI Act europ en : entr en vigueur en août 2024, il impose aux systèmes d'IA à haut risque — dont plusieurs usages bancaires comme le scoring de cr dit — des obligations de gestion des risques, de gouvernance des donn es, de documentation technique, de supervision humaine et de surveillance post-d ploiement. Le calendrier pr cis de mise en application de ces obligations pour le secteur financier continue d' voluer dans le cadre des discussions sur le « Digital Omnibus » europ en, ce qui impose une veille r glementaire active. DORA : en vigueur depuis janvier 2025, il impose un cadre de gestion du risque ICT, un registre des prestataires tiers, un reporting d'incidents et des tests de r silience — et couvre explicitement les systèmes d'IA en tant qu'actifs ICT. Bâle III/IV, ECB, EBA : ces cadres prudentiels intègrent progressivement des attentes sur la gouvernance des modèles, y compris ceux fond s sur l'IA, dans la continuit du risk management model existant (SR 11-7 et quivalents). ISO/IEC 42001 et NIST AI RMF : ces r f rentiels internationaux, bien que non contraignants juridiquement en Europe, deviennent des standards de facto pour structurer un système de management de l'IA et d montrer une gouvernance robuste face aux superviseurs. Le message commun de ces cadres est sans ambiguït : l'autonomie croissante des systèmes d'IA doit s'accompagner d'une supervision humaine renforc e, pas all g e. Bonnes pratiques : bâtir une gouvernance de l'IA qui inspire confiance Une gouvernance responsable de l'IA dans le risque op rationnel repose sur des piliers d sormais bien identifi s par l'industrie : Un comit IA transverse, associant Risk, Compliance, IT et m tiers, avec un mandat clair de validation des cas d'usage. Une politique IA formalis e, d finissant les usages autoris s, interdits et soumis à validation renforc e. Un registre des modèles, recensant chaque système d'IA, sa finalit , son niveau de risque, ses donn es d'entr e et son propri taire responsable. Une validation ind pendante des modèles, r alis e par une quipe distincte de celle qui les a d velopp s, incluant tests de robustesse et analyse d' quit . Une supervision humaine effective, en particulier sur les d cisions à fort impact (cr dit, fraude, conformit ). Une gestion active des biais, avec des tests r guliers sur des donn es repr sentatives. Des indicateurs de performance et de d rive, suivis dans la dur e et non uniquement lors de la mise en production. Un audit r gulier des modèles, int gr au plan d'audit interne global. Une documentation exhaustive, condition sine qua non pour satisfaire simultan ment les exigences de l'AI Act et de DORA. Un plan de formation des quipes Risk, Compliance et m tiers à la compr hension — non à l'ing nierie — des systèmes d'IA qu'elles supervisent. Le rôle du Risk Manager de demain La fonction risque op rationnel est en train de se transformer en profondeur. Le Risk Manager de demain devra conjuguer plusieurs identit s : AI Risk Manager, capable d' valuer le risque sp cifique d'un système d'IA, au-delà des cat gories traditionnelles. Data-driven Risk Manager, à l'aise avec l'exploitation de donn es massives et h t rogènes. Sp cialiste du Continuous Risk Monitoring, pilotant des dispositifs de surveillance en temps r el plutôt que des contrôles p riodiques. Acteur du Model Risk Management, appliquant aux modèles d'IA la même rigueur m thodologique que celle historiquement r serv e aux modèles de cr dit ou de march . Contributeur actif de l'AI Governance, aux côt s des fonctions juridiques, techniques et m tiers. Les comp tences attendues voluent en cons quence : compr hension des principes du machine learning, culture r glementaire IA, capacit à dialoguer avec les quipes data science, et surtout un sens critique renforc face aux r sultats produits par les systèmes automatis s. Tableau synth tique : opportunit s et risques de l'IA dans le risque op rationnel bancaire Dimension Opportunit s Risques D tection de fraude Identification en temps r el, r duction des faux positifs Fraude assist e par IA, deepfakes Conformit r glementaire Automatisation des rapports, gain de temps Hallucinations, erreurs non d tect es Prise de d cision Aide à la d cision, scoring dynamique Biais algorithmiques, manque d'explicabilit Coûts R duction des tâches manuelles à faible valeur Coûts d'impl mentation et de gouvernance lev s R silience op rationnelle Surveillance continue, d tection pr coce D pendance technologique, risque fournisseur R glementation Cadres structurants (AI Act, DORA) Complexit de mise en conformit multi-r gimes Capital humain Mont e en comp tences, nouveaux rôles R sistance au changement, dilution des responsabilit s Conclusion : une transformation à piloter, pas à subir L'Intelligence Artificielle ne constitue ni une baguette magique ni une menace existentielle pour la gestion du risque op rationnel bancaire. Elle est un acc l rateur puissant, à condition d'être encadr e par une gouvernance à la hauteur de sa capacit de transformation. L'IA ne remplacera probablement pas les gestionnaires des risques. En revanche, les gestionnaires des risques qui maîtrisent l'IA remplaceront ceux qui l'ignorent. Les tablissements qui sauront conjuguer ambition technologique, rigueur de gouvernance et conformit r glementaire ne se contenteront pas de r duire leurs pertes op rationnelles : ils construiront un avantage concurrentiel durable, fond sur la confiance. Cinq enseignements cl s L'adoption de l'IA dans le risque op rationnel bancaire n'est plus une option diff renciante : elle devient un standard de march . Les gains les plus tangibles se concentrent aujourd'hui sur la fraude, l'AML et l'automatisation des contrôles. Les risques introduits par l'IA — biais, hallucinations, d pendance fournisseur — appartiennent pleinement au p rimètre du risque op rationnel et doivent être trait s comme tels. AI Act et DORA imposent d sormais un double cadre de conformit qui exige une documentation et une gouvernance int gr es, et non juxtapos es. Le Risk Manager de demain sera autant un expert en gouvernance qu'un interlocuteur cr dible des quipes data et technologie. Et vous, où en est votre organisation dans la structuration de sa gouvernance IA appliqu e au risque op rationnel ? Quels cas d'usage avez-vous d jà d ploy s, et quels obstacles rencontrez-vous ? Partagez votre retour d'exp rience en commentaire — cet change nourrit une r flexion collective dont notre secteur a besoin. Sources cit es : McKinsey & Company (State of AI Trust 2026 ; Global Banking Annual Review 2026 ; Banking’s AI angst) ; Deloitte (AI Adoption in Financial Institutions — EMEA MRM Survey 2025 ; 2026 Banking & Capital Markets Outlook) ; Mastercard / Financial Times Longitude (2025 Payment Fraud Prevention Report) ; Commission europ enne (AI Act) ; r glementation DORA (UE 2022/2554).
by Youness El Kandoussi | 3 months ago | 0 Comment(s) | 214 Share(s) | Tags :

Contents 1 Abstract.. 4 2 Introduction.. 4 3 Objective: 5 4 Plan of the paper: 5 5 Chapter 1: Risk History and definitions. 5 5.1 Introduction: 5 5.2 Section I: Risk Management History: 6 5.3 Section 2: Definitions of Risk Management: 7 5.3.1 Market Risk: 8 5.3.2 Credit Risk. 8 5.3.3 Liquidity Risk: 8 5.3.4 Operational Risk: 9 6 Chapter 2: Evolvement of Risk Management: Basel I, II and III. 10 6.1 Introduction: 10 6.2 Section I: Basel I and its shortcomings: 11 6.3 Section 2: Basel II 12 6.4 Section 3: Basel III 13 6.4.1 Summary OF changes. 13 7 Chapter 3: Risk in Islamic Finance Institutions. 14 7.1 Introduction: 14 7.2 Section 1: Islamic Finance Institutions are unique. 16 7.3 Section 2: Types of Risks in the IFIs: 17 8 Chapter 4: Islamic Finance Products, Risks and the key challenges. 19 8.1 Introduction: 19 8.2 Section 1: Risks in Islamic Finance Products: 19 8.2.1 Risks in Musharakah Contracts: 21 8.2.2 Risks in Mudarabah contract: 22 8.2.3 Risks in Murabahah Contract: 24 8.2.4 Risks in Salam Contract: 24 8.2.5 Risks in Istisnaa Contract 25 8.2.6 Risks in Iajrah Contract: 26 8.3 Section 2: Challenges of Risk Management in Islamic Finance Products. 27 9 Chapter 5: Operational Risk in Islamic Finance Institutions. 28 9.1 Introduction: 28 9.2 Section 1: Operational Risk in Musharakah contract: 28 9.3 Section 2: Operational Risk in Mudarabah contract. 29 9.4 Section 3: Operational Risk in Murabahah contract. 29 9.5 Operational Risk in Salam contract. 30 9.6 Operational Risk in Istisnaa contract: 30 9.7 Operational Risk in Ijarah contract: 30 10 Conclusion.. 30 10.1 Findings. 30 10.2 Recommendations. 31 11 References. 33 1 Abstract As IFIs are growing extensively and expected to grow up to 15% in the coming years, it is primordial that all the industry stakeholders start to invest their efforts to develop the Risk Management disciplines. The IFSB and AAOIFI are not sparing any effort to guide and participate in shaping the IF Risk Management, however, they tend to be inspired by the existing frameworks historically developed for Conventional Banks. Islamic Finance contracts are very different in nature and in substance from conventional banks, thus, the conventional Risk Management cannot cater for their uniqueness. This paper tried to highlight uniqueness of risk aspects within the IF contracts, and focused on Operational Risk, which is in my opinion in the major risk for IFI. 2 Introduction Risk Management have evolved since its first appearance after the World War II. The Bank of International Settlement have tried to adapt to the changes in the Finance industry and issued 3 version of the Basel Guidelines on Capital Requirements (Basel I, II and III). These guidelines have identified Capital Requirements for Credit Risk, Market Risk and Operational Risk. They also issued Sound Practices for Risk Management for each type of Risk. With the venue of the Islamic Finance Industry in the 1960s, Risk Management tools had to adapt to the uniqueness of their products. IFSB and AOIIFI have invested huge efforts in developing Risk Management guidelines for IFIs. Scholars and Islamic Finance practitioners issued multitude of papers attempting to circle aspects of Risk in the Islamic Finance Contracts. They have demonstrated that Islamic Finance encompasses other types of Risk that are unknown to conventional Banks (Fiduciary Risk, Sharia non-compliance Risk, Commercial Displaced Risk, etc.) Many of those scholars have also found out that the IFIs are more exposed to Operational Risk than the conventional banks, mainly due to the complexity of the contracts and their execution. This research is an attempt to add some more light on Risks faced by Islamic Finance Institution with a special focus on Operational Risk. 3 Objective: Risk Management in IFIs tends to be complex and least understood by the business and even by the Risk Management practitioners, in this research I will attempt to define Risks in IFIs and clarify its specifications by demonstrating its uniqueness, especially in the Islamic Finance contracts, where each contract can encompass more than one type of Risk. I will also try to cover some more details of Operational Risk aspects in the IF contracts and demonstrate its importance and complexity during the lifecycle. That being discussed I will propose some actions that can enhance the Operational Risk Management within the IFIs. 4 Plan of the paper: In this paper, I will be defining Risk Management in general in Financial Institutions and its degree of evolvement especially in conventional banking, how Risk is different in Islamic Financial Institutions from conventional banks, their instruments and what are the key challenges. Then I will be discussing the Operational Risk Management in Islamic Finance Institutions and its specifications. 5 Chapter 1: Risk History and definitions 5.1 Introduction: Risk Management emerged after the World War II, and began to be studied in universities as a discipline with the two academic books ( Mehr and Hedges (1963) and Williams and Hems (1964)[1]. Risk Management was, for a long time, the ultimate tool for Insurance Industry aiming to mitigate Risks related to individuals and companies from losses incurred from accidents[2] After 1950s, and due to the increasing costs of insurance, various Risk Management activities were introduced to the business (e.g. business continuity, self-insurance). Derivatives were introduced after 1970s to mitigate the faced risks. Market, Credit, and Operational Risk Management tools were introduced to manage the emerging risks from the intensified activities with insurance and Finance industries (consequently after 1980s for Market and Credit and 1990s for Operational Risk)[3] The objective of a financial institution (or for any kind of business) is to maximize shareholders’ profits by adding value and best usage of available resources. Financial institutions, in particular, have to manage Risks to achieve the aforesaid objective. Risk is defined as a possible adverse, one or more, outcomes, it is unknown for its intrinsic volatility and unpredictability. Financial institutions face different types of Risks. Business Risks, which “arises from the nature of a firm’s business. It relates to factors affecting the product market. Financial risk arises from possible losses in financial markets due to movements in financial variables [4]”. Oldfield and Santomero classifies Risk in three types: risks that can be eliminated, those that can be transferred to others, and the risks that can be managed by the institution. [5]” Besides the above given definitions, Risk can also be defined as Financial Risk, i.e. Credit Risk and Market Risk, and non-Financial Risk, i.e., among others, Operational Risk, Legal Risk, Reputational Risk and Strategic Risk.[6] 5.2 Section I: Risk Management History: Risk Management historically was the main objective of the insurance industry. After the World War II, large companies started to mitigate their risks by introducing Self-Insurance techniques. It was largely applied to cover adverse financial impacts consequent of events of losses or Market volatility. After 1970s, Financial Risk Management emerges as a cornerstone for multitude of companies including banks. In Fact, Stock Market prices, exchange rates, commodity prices, were their main concerns. Table 1: Milestones in the History of Risk Management[7] In 1990s Risk Management took more momentum and became a high priority matter for corporates, Board of Director have now the responsibility of oversight and monitoring policies effected by the Board Audit and Risk Management Committees. Financial Institution, after 2000s are required to implement capital reserves for risks, especially after the major defaults and the Enron bankruptcy case. Basel II (2004) issued guidelines on more robust capital requirements on banks for Credit Risk, also introduced rules on managing Operational Risk. In 2010 Basel III came as a response to the 2008 subprime crisis, with more constraints on capital requirements and new Liquidity Risk Management guidelines. 5.3 Section 2: Definitions of Risk Management: According to Wikipedia, “Risk management is the identification, assessment, and prioritization of risks (defined in ISO 31000 as the effect of uncertainty on objectives) followed by coordinated and economical application of resources to minimize, monitor, and control the probability and/or impact of unfortunate events[8] or to maximize the realization of opportunities. Risk management’s objective is to assure uncertainty does not deflect the endeavor from the business goals.[9]” Financial Institutions face generally two types of Risk, Financial and Non-Financial[10] (Gleason 2000). Financial Risks are those due Market volatility (Market Risk), and those due customers’ defaults (Credit Risk). Non-Financial Risk includes, but not limited to, Operational Risk, Legal Risk, Reputational Risk, Regulatory Compliance Risk. 5.3.1 Market Risk: Market Risk is defined as the risk from adverse volatility of traded instruments and assets in a well-defined Market[11]. Market Risk can affect both banking and trading books. In the sense that it is originated from equity price risk, interest rate risk, currency risk, and commodity price risk. Market Risk is said systematic when it arises due to the general volatility of prices and overall changes in policies in the economy. When the price of a specific asset or instruments changes due to events inherent to it, it is categorized as unsystematic Risk. 5.3.2 Credit Risk “Credit risk is most simply defined as the potential that a bank borrower or counterparty will fail to meet its obligations in accordance with agreed terms. The goal of credit risk management is to maximize a bank's risk-adjusted rate of return by maintaining credit risk exposure within acceptable parameters. Banks need to manage the credit risk inherent in the entire portfolio as well as the risk in individual credits or transactions. Banks should also consider the relationships between credit risk and other risks. The effective management of credit risk is a critical component of a comprehensive approach to risk management and essential to the long-term success of any banking organization.”[12] Credit Risk is the risk that counterparty will fail to meet its obligations timely and fully in accordance with the agreed terms[13]. 5.3.3 Liquidity Risk: The Principles for Sound Liquidity Risk Management and Supervision[14] (BCBS 2008) defines Liquidity as “the ability of a bank to fund increases in assets and meet obligations as they come due, without incurring unacceptable losses.” Liquidity Risk arises then from adverse circumstances that hurdles a bank to normally operate and meet its liabilities when due. Funding Liquidity Risk occurs when banks are unable to secure funds at a reasonable cost from borrowing, Asset Liquidity Risk arises when banks face difficulties to generate liquidity from sale of assets.[15] 5.3.4 Operational Risk: The BCBS Principles for the Sound Management of Operational Risk defines Operational Risk as the risk of loss resulting from inadequate or failed internal processes, people and systems or from external events. This definition includes legal risk, but excludes strategic and reputational risk.[16] Operational Risk was for a long time out of the radar of the corporates and scholars, it was not quite understood. Power writes: “Operational risk was conceived as a composite term for a wide variety of organizational and behavioural risk issues which were traditionally excluded from formal definitions of market and credit risk. The explosion of operational risk discourse gave new structure and rationality to what had traditionally been regarded as a risk management residual and negatively described as non-financial risk.”[17] The Bank of international Settlements (BIS) have categorized Operational Risk into four causal categories[18]: · Process · Business Process (lack of proper due diligence, inadequate/problematic account reconciliation, etc.) · Business Risks (merger risk, new product risk, etc.) · Errors and Omissions (inadequate/problematic security, inadequate/problematic quality control, etc.) · Specific Liabilities (employee benefits, employer, directors and officers, etc.) · People · Employee Errors (general transaction errors, incorrect routing of transaction, etc.) · Human Resource Issues (employee unavailability, hiring/firing, etc.) · Personal Injury – Physical Injury (bodily injury, health and safety, etc.) Personal Injury – Non–Physical Injury (libel/defamation/slander, discrimination/harassment, etc.) · Wrongful Acts (fraud, trading misdeeds, etc.) · Information Technology · General Technology Problems (operational error – technology related, unauthorized use/misuse of technology, etc.) · Hardware (equipment failure, inadequate/unavailable hardware, etc.) · Security (hacking, firewall failure, external disruption, etc.) · Software (computer virus, programming bug, etc.) · Systems (system failures, system maintenance, etc.) · Telecommunications (telephone, fax, etc.) · External Events · Disasters (natural disasters, non–natural disasters, etc.) · External Misdeeds (external fraud, external money laundering, etc.) · Litigation/Regulation (capital control, regulatory change, legal change, etc.) · Relationships · Legal/Contractual (securities law violations, legal liabilities, etc.) · Negligence (gross negligence, general negligence, etc.) · Sales Discrimination (lending discrimination, client Discrimination, etc.) · Sales Related Issues (churning, sales misrepresentation, high pressure sales tactics, etc.) · Specific Omissions (failure to pay proper fees, failure to file proper report, etc.) Gene Alvares attempted a mapping exercise between the Causal Categories and Basel Risk Types (Alvares, Global Association of Risk Professionals GARP studies. 2002). Mapping illustration between the Basel Committee’s proposed operational risk event classification scheme and Zurich IC2 format. (Alvarez, 2002)[19] References Georges Dionne, Risk Management: History and Critique, March 2013 Harrington and Neihaus, 2013, Georges Dionne, Risk Management: History and Critique, March 2013 Jorion and Khoury 1996, reference cited by Tariqullah Khan Habib Ahmed: Risk Management: An Analysis Of Issues In Islamic Financial Industry, 2001, Islamic Development Bank, Islamic Research and Training Institute Oldfield and Santomero (1997), reference cited by Tariqullah Khan Habib Ahmed: Risk Management: An Analysis Of Issues In Islamic Financial Industry, 2001, , Islamic Development Bank, Islamic Research and Training Institute Tariqullah Khan Habib Ahmed: Risk Management: An Analysis Of Issues In Islamic Financial Industry, 2001, Islamic Development Bank, Islamic Research and Training Institute Hubbard, Douglas (2009). The Failure of Risk Management: Why It's Broken and How to Fix It. John Wiley & Sons. (Wikipedia) Antunes, Ricardo; Gonzalez, Vicente (3 March 2015). "A Production Model for Construction: A Theoretical Framework". Buildings. 5 (1): 209–228. doi:10.3390/buildings5010209. (Wikipedia) BCBS - Principles for the Management of Credit Risk - final document, September 2000 BCBS - Principles for Sound Liquidity Risk Management and Supervision - final document, September 2008 BCBS Principles for the Sound Management of Operational Risk, 2011 Power p. 103 Cited by Johannes Gaus aus Böblingen, The Risks of Financial Risk Management, Master-Thesis, Economics of Financial Institutions European Business School, Department Corporate Management & Economics, Zeppelin University Marinoiu Ana Maria, Bucharest University of Economics, Faculty of International Business and Economics, Operational Risk In International Business: Taxonomy And Assessment Methods, Federal Reserve Bulletin, September 2003, Capital Standards for Banks: The Evolving Basel Accord BCBS, Basel II: The New Basel Capital Accord - third consultative paper April 2003 and Revised international capital framework, June 2006 Basel III: international regulatory framework for banks Sean Kenny, To What Extent were the Limitations of the Previous Basel Accords (I & II) overlooked by Basel III?, Master programme in Economic History, Lund University, School of Economics and Management, June 2011 BCBS- Pillar 2 (Supervisory Review Process), the New Basel Capital Accord, Principal 2 Basel II, Tamer Bakiciol Nicolas Cojocaru-Durand DongxuLu, December 2008 BIS, BCSB, Basel III: international regulatory framework for banks Basel Committee on Banking Supervision, Basel III: International Framework for Liquidity Risk Measurement, Standards and Monitoring, Dec 10, Bank for International Settlements. http://wwww.basel-ii-risk.com/basel-iii-guide-to-the-changes/ Ahmad Alharbi, Development of the Islamic Banking System, Journal of Islamic Banking and Finance June 2015, Vol. 3, No. 1 Syed Ehsan Ullah Agha, RISK MANAGEMENT IN ISLAMIC FINANCE: AN ANALYSIS FROM OBJECTIVES OF SHARI’AH PERSPECTIVE, International Journal of Business, Economics and Law, Vol. 7, Issue 3 (Aug.) 2015 Specifics of Risk Management in Islamic Finance and Banking, with Emphasis on Bosnia and Herzegovina, E.Kozarević, M.Baraković Nurikić & N.Nuhanović, Bahar/Spring 2014, Volume 4, Issue 1, Çankırı Karatekin University, Journal of The Faculty of Economics, and Administrative Sciences. Ioannis Akkizidis and Sunil Kumar Khandelwal, Financial Risk Management for Islamic Banking and Finance, Palgrave Macmillan. Standing Committee for Economic and Commercial Cooperation of the Organization of Islamic Cooperation (COMCEC), Risk Management in Islamic Financial Instruments, COMCEC Coordination Office, September 2014. ISLAMIC FINANCIAL SERVICES BOARD, GUIDING PRINCIPLES OF RISK MANAGEMENT FOR INSTITUTIONS (OTHER THAN INSURANCE INSTITUTIONS) OFFERING ONLY ISLAMIC FINANCIAL SERVICES, December 2005. Nurhafiza Abdul Kader Malim PhD, Islamic Banking and Risk Management: Issues and Challenges, Journal of Islamic Banking and Finance Oct.- Dec. 2015. Hennie van Greuning Zamir Iqbal, Risk Analysis for Islamic Banks, THE WORLD BANK Washington, D.C., December 2008. Ahmad Mohamed Rahim, Operational Risks in Islamic Profit Sharing Contracts and Ways to Overcome Them, MSc in Islamic Finance, The Global University of Islamic Finance, October 2014 (http://www.inceif.org/research-bulletin/operational-risks-islamic-profit-sharing-contracts-ways-overcome/) [1] Georges Dionne, Risk Management: History and Critique, March 2013, p. 1 [2] Harrington and Neihaus, 2013, Georges Dionne, Risk Management: History and Critique, March 2013, p. 1 [3] Georges Dionne, Risk Management: History and Critique, March 2013, p. 1 [4] Jorion and Khoury 1996, p. 2, reference cited by Tariqullah Khan Habib Ahmed: Risk Management: An Analysis Of Issues In Islamic Financial Industry, 2001,p. 26, Islamic Development Bank, Islamic Research and Training Institute [5] Oldfield and Santomero (1997), reference cited by Tariqullah Khan Habib Ahmed: Risk Management: An Analysis Of Issues In Islamic Financial Industry, 2001,p. 27, Islamic Development Bank, Islamic Research and Training Institute [6] Tariqullah Khan Habib Ahmed: Risk Management: An Analysis Of Issues In Islamic Financial Industry, 2001,p. 28, Islamic Development Bank, Islamic Research and Training Institute [7] Georges Dionne, Risk Management: History and Critique, March 2013, p. 6 [8] Hubbard, Douglas (2009). The Failure of Risk Management: Why It's Broken and How to Fix It. John Wiley & Sons. p. 46. (Wikipedia) [9] Antunes, Ricardo; Gonzalez, Vicente (3 March 2015). "A Production Model for Construction: A Theoretical Framework". Buildings. 5 (1): 209–228. doi:10.3390/buildings5010209. (Wikipedia) [10] Tariqullah Khan Habib Ahmed: Risk Management: An Analysis of Issues in Islamic Financial Industry, 2001, p. 28, Islamic Development Bank, Islamic Research and Training Institute [11] Tariqullah Khan Habib Ahmed: Risk Management: An Analysis of Issues in Islamic Financial Industry, 2001, p. 28, Islamic Development Bank, Islamic Research and Training Institute [12] BCBS - Principles for the Management of Credit Risk - final document, September 2000 [13] Tariqullah Khan Habib Ahmed: Risk Management: An Analysis of Issues in Islamic Financial Industry, 2001, p. 29, Islamic Development Bank, Islamic Research and Training Institute [14] BCBS - Principles for Sound Liquidity Risk Management and Supervision - final document, September 2008 [15] Tariqullah Khan Habib Ahmed: Risk Management: An Analysis of Issues in Islamic Financial Industry, 2001, p. 29, Islamic Development Bank, Islamic Research and Training Institute [16] BCBS Principles for the Sound Management of Operational Risk, 2011, p. 3 [17] Power p. 103 Cited by Johannes Gaus aus Böblingen, The Risks of Financial Risk Management, Master-Thesis, Economics of Financial Institutions European Business School, Department Corporate Management & Economics, Zeppelin University, p. 38 [18] Marinoiu Ana Maria, Bucharest University of Economics, Faculty of International Business and Economics, Operational Risk In International Business: Taxonomy And Assessment Methods, P. 196 [19] Marinoiu Ana Maria, Bucharest University of Economics, Faculty of International Business and Economics, Operational Risk in International Business: Taxonomy and Assessment Methods, P. 197
by Youness El Kandoussi | 3 years ago | 0 Comment(s) | 1582 Share(s) | Tags :